
AHA testifies at hearing on health care cybersecurity
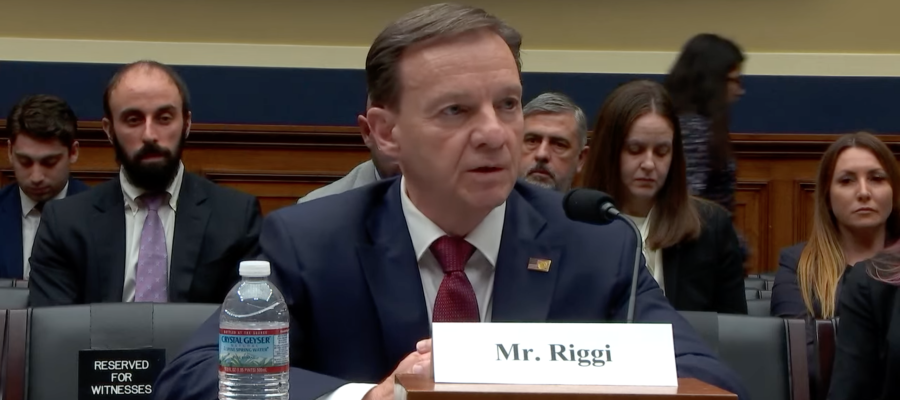
Testifying April 16 before a House Energy and Commerce Subcommittee on Health hearing on addressing health care cybersecurity vulnerabilities in the wake of the Change Healthcare attack, AHA shared proposals and concerns for Congress and the Administration to consider.
“To make meaningful progress in the war on cybercrime, Congress and the Administration should focus on the entire health care sector and not just hospitals,” said John Riggi, AHA’s national advisor for cybersecurity and risk. “Furthermore, for any defensive strategy imposed on the health care sector, Congress should call on federal agencies to protect hospitals and health systems — and the patients they care for — by deploying a strong and sustained offensive cyber strategy to combat this ongoing and unresolved national security threat. Health care is a top critical infrastructure sector with direct impact to public health and safety and must be protected. Any cyberattack on the health care sector that disrupts or delays patient care creates a risk to patient safety and crosses the line from an economic crime to a threat-to-life crime.”
Among other actions, he urged Congress to “address the outstanding issues resulting from the cyberattack on Change Healthcare for the wellbeing of our patients and communities. These include ensuring providers are reconnected to services, are able to process claims and appeal denials, have the information needed to reconcile payments and issue patient bills, and are able to access needed financial support to mitigate the considerable costs incurred by hospitals and health systems as a result of the cyberattack.”
Also testifying at the hearing were Greg Garcia, executive director for cybersecurity at the Healthcare Sector Coordinating Council; Robert Sheldon, senior director of public policy and strategy for CrowdStrike; Scott MacLean, chair of the College of Healthcare Information Management Executives; and Adam Bruggeman, M.D., an orthopedic surgeon at the Texas Spine Center.